
Amsterdam Hacker Arrested: Unveiling the ShinyHunters Threat
Inside the ShinyHunters Investigation and Its Implications
Executive Summary
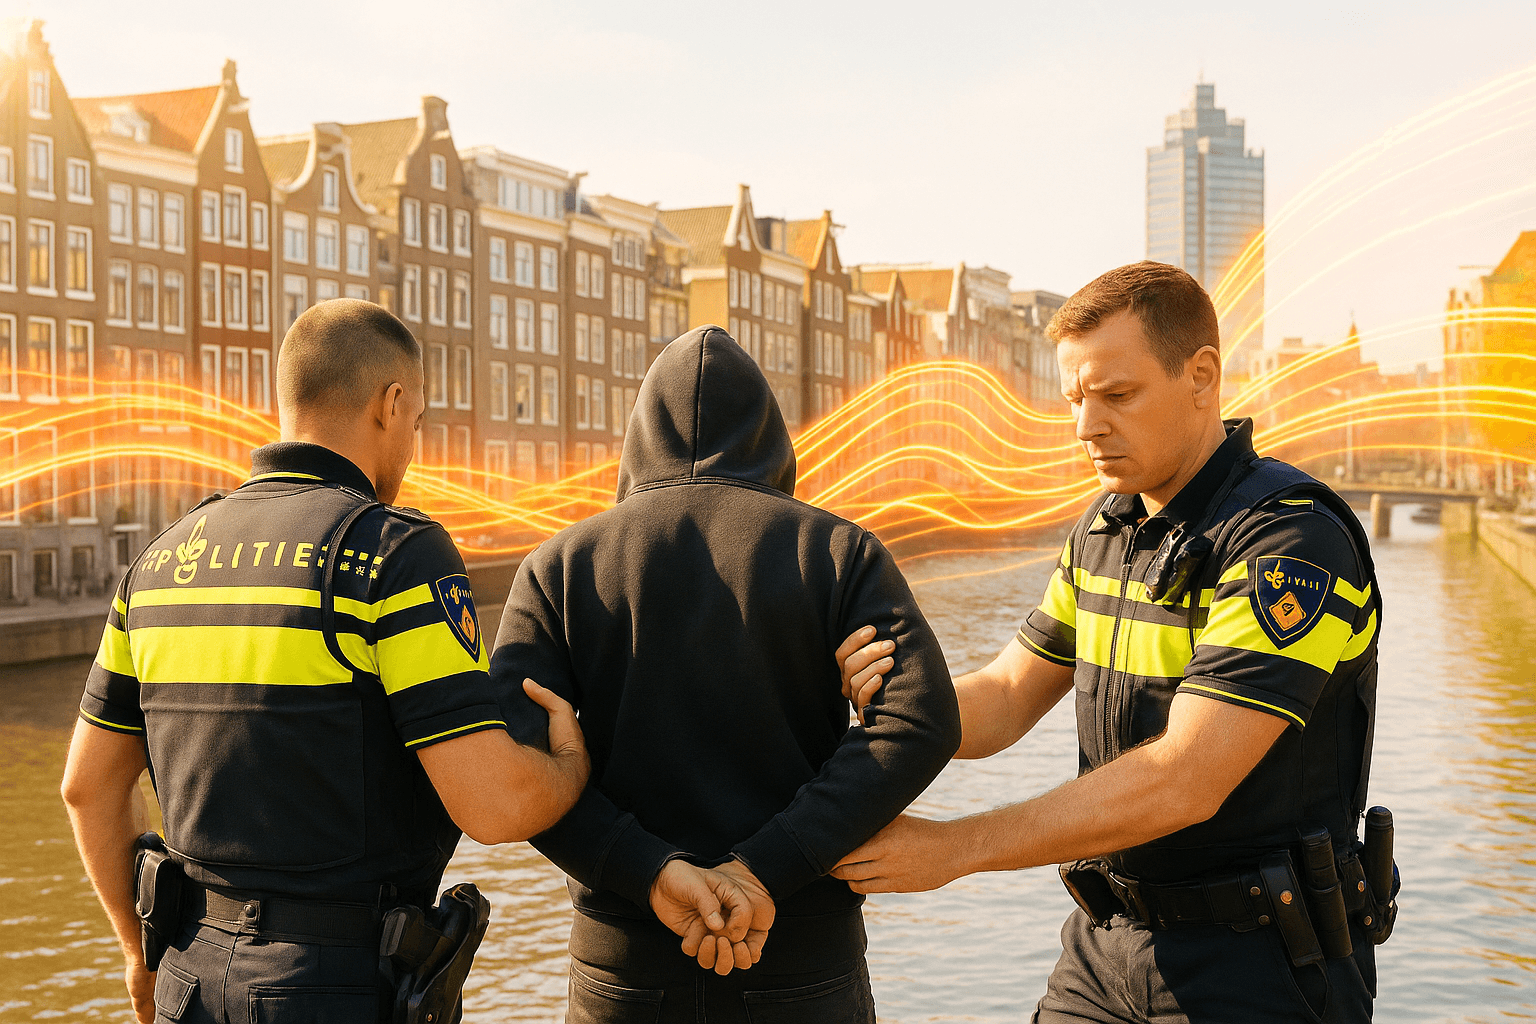
A 24-year-old man from Amsterdam was arrested in connection with the ShinyHunters hacking group. This incident underscores the persistent threat posed by organized cybercriminals targeting sensitive data. Companies must enhance their security measures to protect against potential breaches.
Introduction: Understanding the Threat
The arrest of the Amsterdam man linked to ShinyHunters has drawn significant attention within the cybersecurity community. ShinyHunters, a notorious cybercriminal group, is known for its targeted attacks on high-profile organizations, aiming to steal and sell sensitive data. Understanding why these threats matter is crucial for today's organizations as data breaches can have devastating consequences.
Cyber threats are evolving rapidly, with hacker groups like ShinyHunters becoming more sophisticated. These groups often target companies with valuable data, exploiting vulnerabilities to gain unauthorized access. The arrest highlights the urgent need for organizations to bolster their cybersecurity strategies.
The Threat Landscape: Current State of Affairs
Cybersecurity threats have grown exponentially over the past decade, with the rise of organized groups like ShinyHunters. According to a recent report, data breaches increased by 27% in the past year, affecting millions of users worldwide. The threat landscape is constantly evolving, with new attack methods and vulnerabilities emerging regularly.
ShinyHunters fits into this landscape as a significant player, responsible for multiple high-profile breaches. Their modus operandi involves infiltrating networks, stealing data, and selling it on dark web marketplaces. Recent incidents involving similar groups have shown a pattern of targeting industries with valuable data, such as finance, healthcare, and technology.
Technical Deep Dive: How the Attack Works
ShinyHunters employs various attack vectors to compromise their targets. One common method is exploiting weak credentials through phishing or brute force attacks. Once inside, they often escalate privileges and move laterally across the network to access sensitive data.
Technical indicators of compromise (IOCs) for ShinyHunters include unusual login patterns, unexpected data transfers, and unauthorized access attempts. Cybersecurity teams should also monitor for specific command execution patterns typical of ShinyHunters attacks.
While specific vulnerability details, such as CVEs, are often exploited, the key to their success lies in the meticulous reconnaissance and planning they undertake before launching an attack. Organizations must remain vigilant and keep systems updated to mitigate these risks.
Impact Assessment: Who Is Affected and How
The impact of ShinyHunters' activities is far-reaching, affecting industries such as healthcare, finance, and technology. Data breaches can lead to significant financial losses, reputational damage, and regulatory penalties.
For example, a breach in the healthcare sector could result in the exposure of sensitive patient information, leading to potential legal actions and loss of trust. In the finance sector, unauthorized access to financial records could lead to financial fraud and identity theft.
Organizations must also consider the regulatory implications of data breaches. Compliance with regulations such as GDPR in Europe and CCPA in California is critical to avoid hefty fines and ensure data protection for users.
Real-World Case Studies
In 2020, ShinyHunters was responsible for a breach involving over 73 million user records from various companies. The data was later sold on the dark web, highlighting the group's extensive reach and capabilities.
Another significant incident involved the breach of a major technology company, resulting in the unauthorized access and sale of customer data. These cases demonstrate the urgency for organizations to learn from past attacks and strengthen their defenses.
Mitigation Strategies: Protecting Your Organization
To mitigate the threat posed by groups like ShinyHunters, organizations should implement robust cybersecurity measures. Immediate actions include conducting thorough security audits and patching known vulnerabilities.
Short-term measures involve enhancing authentication protocols, such as implementing multi-factor authentication (MFA), and monitoring network activities for unusual patterns.
Long-term strategies should focus on building a security-conscious culture within the organization. Regular training sessions for employees on recognizing phishing attempts and securing sensitive information are essential.
Specific tools and technologies, such as intrusion detection systems (IDS) and security information and event management (SIEM) solutions, can help in identifying and mitigating potential threats effectively.
Detection and Response
Detecting signs of compromise early is crucial in minimizing the impact of a breach. Indicators include unexpected login attempts, unusual network traffic, and unauthorized data access.
Effective incident response procedures are essential in containing and mitigating the effects of a breach. Organizations should have a dedicated response team and a clear plan for addressing incidents swiftly.
Forensic analysis plays a critical role in understanding the attack's scope and preventing future occurrences. Thorough investigation and documentation of incidents can aid in strengthening defenses against similar attacks.
Expert Insights: Industry Perspective
Leading cybersecurity experts emphasize the importance of staying ahead of evolving threats. The rise of groups like ShinyHunters highlights the need for continuous vigilance and adaptation of security strategies.
Future predictions indicate a shift towards more sophisticated attack methods, leveraging emerging technologies such as AI and machine learning. Security teams must prepare for these advancements by investing in state-of-the-art solutions and continuously updating their knowledge.
Conclusion: Key Takeaways
The arrest of the Amsterdam hacker affiliated with ShinyHunters serves as a stark reminder of the persistent threat posed by organized cybercriminals. Organizations must take proactive measures to protect their data and stay ahead of evolving threats.
- Enhance security protocols with regular audits and updates.
- Implement multi-factor authentication to strengthen access controls.
- Conduct regular employee training on cybersecurity awareness.
- Invest in advanced security tools for real-time threat detection.
- Develop a comprehensive incident response strategy.
- Stay informed on emerging threats and adjust strategies accordingly.
- Collaborate with industry peers to share knowledge and best practices.
Discussion
Share Your Thoughts
Loading comments...
Stay Updated
Subscribe to our newsletter for the latest cybersecurity insights, threat intelligence, and security best practices.