
Covert Espionage Threatens Corporate Privacy: Insights from OpenAI Incident
Understanding and Mitigating Insider Threats in Modern Enterprises
Executive Summary
The recent case involving a former OpenAI engineer accused of espionage highlights vulnerabilities in corporate environments. This article examines the insider threat landscape, provides a technical analysis of the attack, and offers strategies for detection and prevention. Organizations must prioritize securing meeting rooms and sensitive areas to protect against such breaches.
Introduction: Understanding the Threat
In an era where data is king, corporate espionage has become a significant threat to organizations worldwide. The arrest of Abdulrahman Alfozan, a former OpenAI engineer, for allegedly planting a covert listening device in an executive meeting room, serves as a stark reminder of the risks posed by insiders. This incident underscores why businesses must remain vigilant against internal threats that can compromise sensitive information.
Historically, breaches involving insider threats have proven to be particularly damaging due to the perpetrators' inherent knowledge of internal systems and processes. The ability to anticipate security measures and exploit them from within gives internal actors an edge over external attackers. With the increasing value of intellectual property and proprietary data, the stakes for organizations have never been higher.
The Threat Landscape: Current State of Affairs
Insider threats are a growing concern in the cybersecurity landscape. According to a recent report by Verizon, insider incidents account for approximately 34% of data breaches. This statistic highlights the need for organizations to focus not only on external threats but also on potential risks from within their own ranks.
Recent high-profile cases, such as the Capital One breach where a former employee exploited their access, have demonstrated the severe consequences of insider attacks. The OpenAI incident fits into a broader pattern where individuals with privileged access exploit their positions to gather sensitive information.
These threats are not confined to any single industry. From technology firms to financial institutions, any organization possessing valuable data is a potential target. As companies invest in digital transformation, the attack surface continues to expand, necessitating robust security measures.
Technical Deep Dive: How the Attack Works
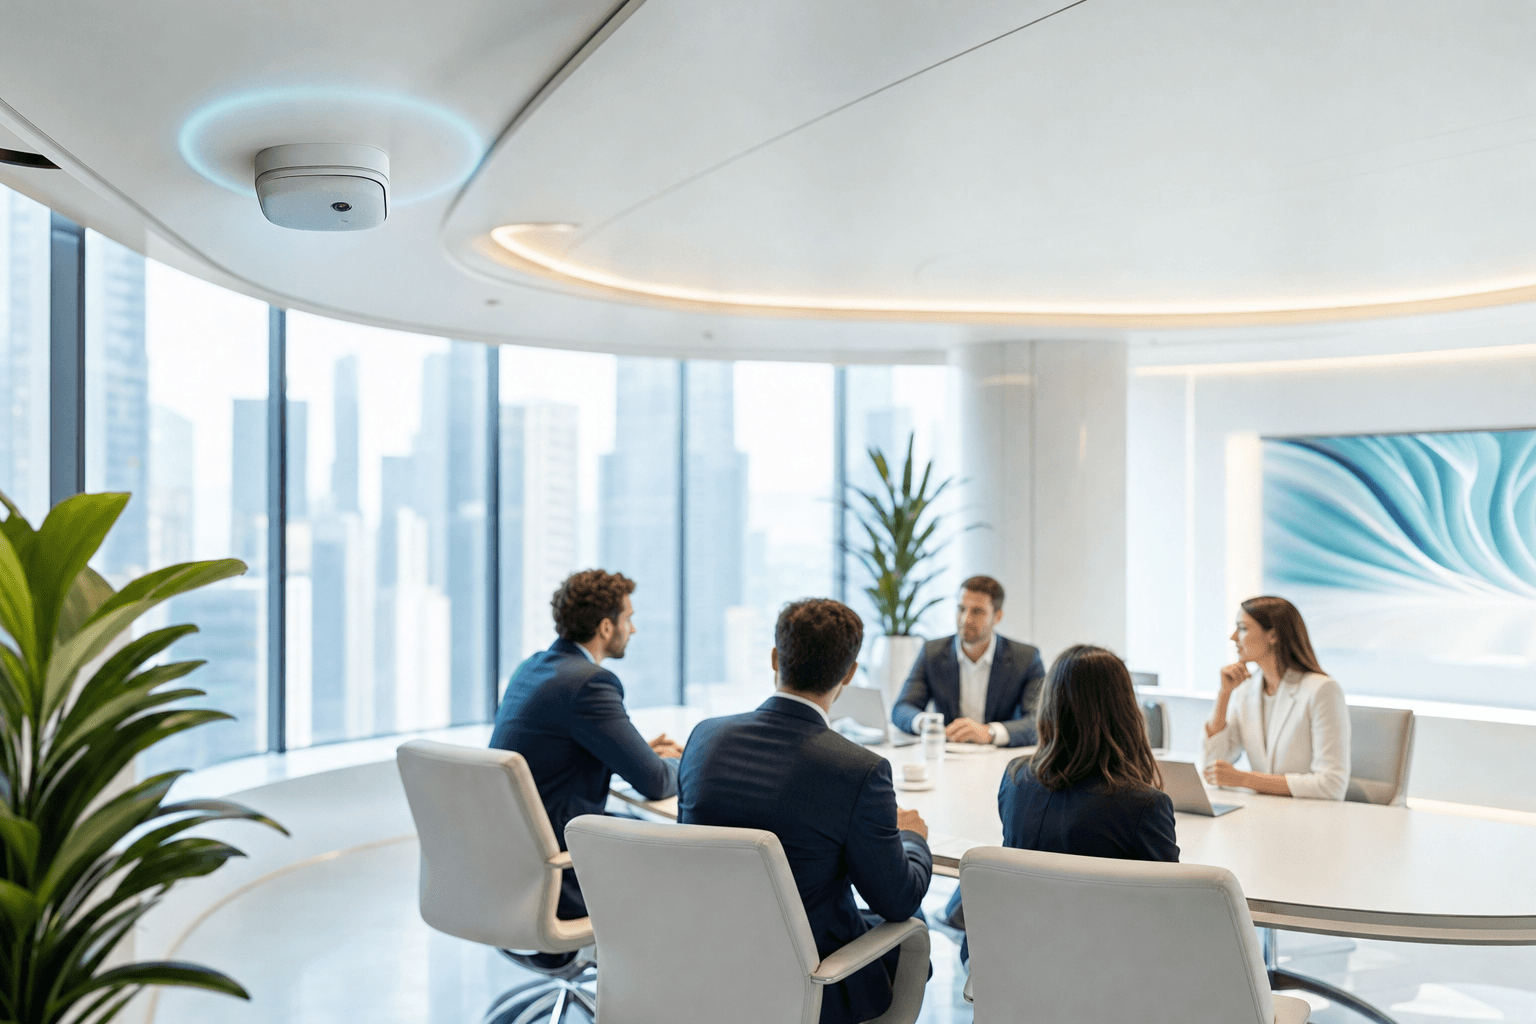
In the OpenAI case, the alleged use of a covert recording device represents a low-tech yet highly effective method of espionage. Such devices can be easily concealed and are capable of capturing high-quality audio, posing a significant risk to privacy and confidentiality.
Attack vectors for insider threats typically involve exploiting legitimate access to systems and data. In this scenario, the device was likely planted during routine access to the meeting room. Indicators of compromise (IOCs) for such attacks may include unexpected device connections or unusual traffic patterns on the network.
While this particular incident did not involve advanced malware or hacking techniques, it underscores the importance of physical security and access control. Organizations should consider implementing measures such as regular sweeps for unauthorized devices, especially in areas where sensitive discussions occur.
Impact Assessment: Who Is Affected and How
The ramifications of such incidents extend beyond the immediate organization. Industries that rely heavily on intellectual property, such as technology and pharmaceuticals, are particularly vulnerable to espionage activities.
Financially, the costs associated with insider threats can be substantial. According to the Ponemon Institute, the average cost of an insider threat incident is $11.45 million. These costs include legal fees, regulatory fines, and the loss of competitive advantage.
From a compliance perspective, organizations must adhere to regulations such as the General Data Protection Regulation (GDPR) and the California Consumer Privacy Act (CCPA) to protect personal data. Breaches can lead to significant penalties and damage to reputation.
Real-World Case Studies
One notable example of an insider threat is the Edward Snowden case, where a former NSA contractor leaked classified information. This incident highlighted the need for stringent access controls and monitoring.
Another case involves the Tesla employee who was accused of stealing trade secrets. Such incidents emphasize the importance of safeguarding intellectual property through robust internal policies and employee training.
Mitigation Strategies: Protecting Your Organization
Organizations can take several steps to mitigate the risk of insider threats. Immediate actions include conducting thorough background checks during hiring and implementing strict access controls.
Short-term measures involve educating employees about the importance of data security and establishing clear protocols for reporting suspicious behavior. Organizations should also regularly review and update their security policies to reflect the evolving threat landscape.
Long-term strategies focus on creating a security culture within the organization. This includes fostering an environment of trust where employees feel comfortable reporting potential threats without fear of retribution.
Detection and Response
Detecting insider threats requires a combination of technical and human-centric approaches. Anomalies in user behavior, such as accessing sensitive data outside of regular working hours, can serve as red flags.
Organizations should implement continuous monitoring systems to detect suspicious activities and conduct regular audits of access logs. In the event of a suspected breach, a well-defined incident response plan is crucial to minimize damage and restore normal operations.
Expert Insights: Industry Perspective
Experts predict that as organizations continue to digitalize, insider threats will become more sophisticated. Security teams must stay ahead by leveraging advanced analytics and artificial intelligence to identify potential threats.
The evolving threat landscape requires a proactive approach to cybersecurity. Organizations must invest in both technology and personnel to effectively combat insider threats and protect their assets.
Conclusion: Key Takeaways
The OpenAI incident serves as a reminder of the persistent threat of corporate espionage. Organizations must prioritize security measures to protect against insider threats.
- Implement strict access controls and regular security audits.
- Foster a security-oriented culture within the organization.
- Utilize advanced monitoring tools to detect anomalies.
- Develop and regularly update an incident response plan.
- Ensure compliance with relevant data protection regulations.
Keep reading
Discussion
Share Your Thoughts
Loading comments...
Stay Updated
Subscribe to our newsletter for the latest cybersecurity insights, threat intelligence, and security best practices.