
Cyberattack Heats French Supermarkets: Lessons in IoT Vulnerability
Understanding IoT threats in the food retail industry
Executive Summary
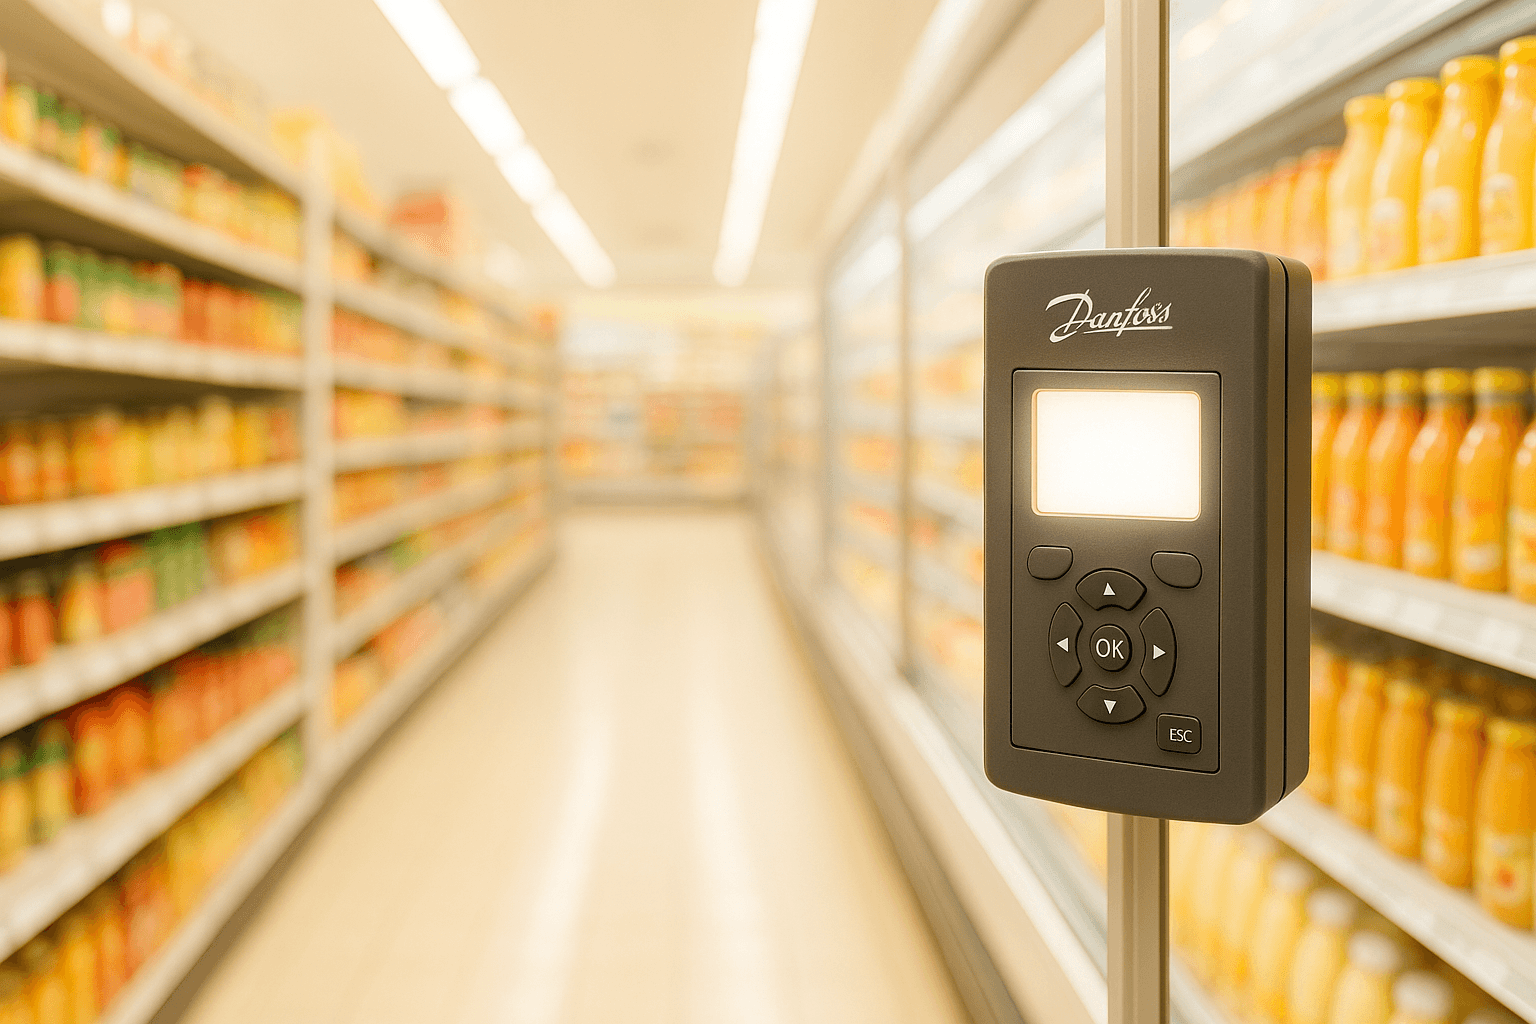
On the night of October 11, attackers remotely hijacked Danfoss controllers in French supermarkets, heating fridges to 50°C and causing significant food wastage. This incident underscores vulnerabilities in IoT systems and the critical need for enhanced security protocols to prevent future breaches. Organizations must prioritize securing IoT devices with robust strategies.
Introduction: Understanding the Threat
The recent cyberattack on French supermarkets showcases the growing threat landscape of IoT vulnerabilities. As technology integrates deeper into everyday operations, organizations must recognize the potential risks associated with connected devices. The manipulation of Danfoss controllers is not just a localized issue but a wake-up call for industries worldwide.
Historically, similar incidents have demonstrated the fragility of IoT devices. In 2016, the Mirai botnet attack exploited weak IoT security, affecting internet connectivity globally. Such events highlight the critical need for robust security measures in IoT deployment.
The Threat Landscape: Current State of Affairs
The proliferation of IoT devices has reshaped the cybersecurity landscape. According to Gartner, the number of connected devices is expected to reach 25 billion by 2025. This expansion presents an attractive target for malicious actors seeking to exploit vulnerabilities.
The food retail industry is particularly susceptible, given its reliance on automated systems for efficiency. The Danfoss controller breach is part of a broader trend where attackers target weak links in supply chains, aiming for maximum disruption.
Recent incidents, such as the Colonial Pipeline attack, further illustrate how cyber threats can disrupt critical operations. Understanding these patterns is vital for developing effective security strategies.
Technical Deep Dive: How the Attack Works
The attackers exploited vulnerabilities within the Danfoss controllers, devices commonly used to manage refrigeration systems in supermarkets. These controllers, accessible via remote management interfaces, were targeted by the attackers using known vulnerabilities.
Once inside the system, attackers manipulated temperature settings, raising them to 50°C. This exploitation was likely achieved through weak authentication protocols, allowing unauthorized access.
The attack vectors included exploiting default credentials and unpatched firmware vulnerabilities. Technical indicators of compromise (IOCs) include unusual login attempts and unexpected configuration changes.
While no specific CVE numbers have been released, similar vulnerabilities have been documented in other IoT devices, emphasizing the need for timely patching and updates.
Impact Assessment: Who Is Affected and How
The primary industries affected include food retail and supply chain logistics. The financial implications are significant, with potential losses from wasted inventory and disrupted operations running into millions.
Operationally, the affected supermarkets faced immediate issues with inventory management and customer dissatisfaction. The reputational damage can also have long-term effects on consumer trust.
From a regulatory standpoint, compliance with data protection and consumer safety regulations is a concern, highlighting the need for organizations to have robust data protection measures in place.
Real-World Case Studies
In 2020, a similar attack targeted smart thermostats in the hospitality industry, manipulating room temperatures and causing guest discomfort. The incident underscored the importance of securing remote access to IoT systems.
Lessons from these cases emphasize the need for comprehensive security policies and regular audits to ensure IoT device integrity. Organizations must learn from these examples to bolster their defenses.
Mitigation Strategies: Protecting Your Organization
Organizations should immediately conduct security audits of all IoT devices, ensuring firmware is up-to-date and default credentials are changed. Implementing network segmentation can also limit the spread of potential breaches.
Short-term measures include enhancing authentication protocols and enabling multi-factor authentication (MFA) for remote access. Regularly updating software and conducting vulnerability assessments are crucial.
Long-term strategies involve investing in IoT security training for staff and adopting AI-driven threat detection technologies. Collaborating with industry partners for threat intelligence sharing can also enhance security posture.
Consider utilizing tools like SIEM (Security Information and Event Management) systems for real-time monitoring and incident response.
Detection and Response
Detection methods include monitoring for unusual network activity and implementing intrusion detection systems (IDS) to identify unauthorized access attempts.
Signs of compromise include unexpected device behavior and anomalous configuration changes. Having a robust incident response plan that includes immediate disconnection of compromised devices is essential.
Forensic analysis post-incident can help determine the attack's origin and scope, aiding in future prevention efforts.
Expert Insights: Industry Perspective
Industry experts predict an increase in IoT-targeted attacks as devices become more integrated into critical operations. Organizations must prepare for evolving threats by adopting proactive security measures.
The future landscape will likely see a shift towards more sophisticated attack techniques, necessitating continuous adaptation of security strategies. Emphasizing security by design in IoT device development is crucial.
Conclusion: Key Takeaways
The French supermarket attack serves as a stark reminder of the risks associated with IoT vulnerabilities. By adopting comprehensive security measures, organizations can better protect themselves against future threats.
- Conduct regular IoT security audits.
- Update device firmware promptly and change default credentials.
- Implement network segmentation and MFA.
- Invest in AI-driven threat detection technologies.
- Develop a robust incident response plan.
Discussion
Share Your Thoughts
Loading comments...
Stay Updated
Subscribe to our newsletter for the latest cybersecurity insights, threat intelligence, and security best practices.