
North Korean Hackers Exploit Deepfake Videos to Steal $400M in Crypto
Unmasking the FaceStealer Scheme and Its Impact on Cybersecurity
Executive Summary
North Korean hackers, leveraging advanced deepfake video technology, have stolen over $400 million in cryptocurrency through a scheme called FaceStealer. This incident highlights the growing sophistication of social engineering attacks and poses significant risks to organizations worldwide. To mitigate such threats, companies need to enhance their cybersecurity defenses and remain vigilant against evolving attack vectors.
Introduction: Understanding the Threat
The recent revelation by the FBI about North Korean hackers using deepfake video calls to steal cryptocurrency has sent shockwaves across the cybersecurity landscape. This attack, codenamed FaceStealer, is a stark reminder of the evolving tactics employed by threat actors. As organizations increasingly rely on remote communication, the potential for exploitation through deepfake technology becomes a pressing concern.
Historically, social engineering attacks have been a favored method for cybercriminals. However, the integration of deepfake technology represents a new frontier, combining artificial intelligence with traditional phishing techniques to create convincing fraudulent scenarios. This development necessitates a reevaluation of existing security protocols and a proactive approach to emerging threats.
The Threat Landscape: Current State of Affairs
The global cybersecurity landscape is witnessing a surge in sophisticated attacks, with social engineering emerging as a predominant vector. According to industry reports, social engineering attacks account for over 70% of successful breaches, with deepfakes becoming a notable tool in the attackers' arsenal. These attacks exploit human vulnerabilities, making them particularly challenging to defend against.
Recent incidents, such as the FaceStealer scheme, underscore the importance of understanding the broader threat landscape. In a digital world where authenticity is increasingly questioned, organizations must be equipped to identify and mitigate threats that leverage emerging technologies like deepfakes. The integration of machine learning and AI into cyberattacks is not only a challenge but also an opportunity for defenders to innovate and enhance their security measures.
Technical Deep Dive: How the Attack Works
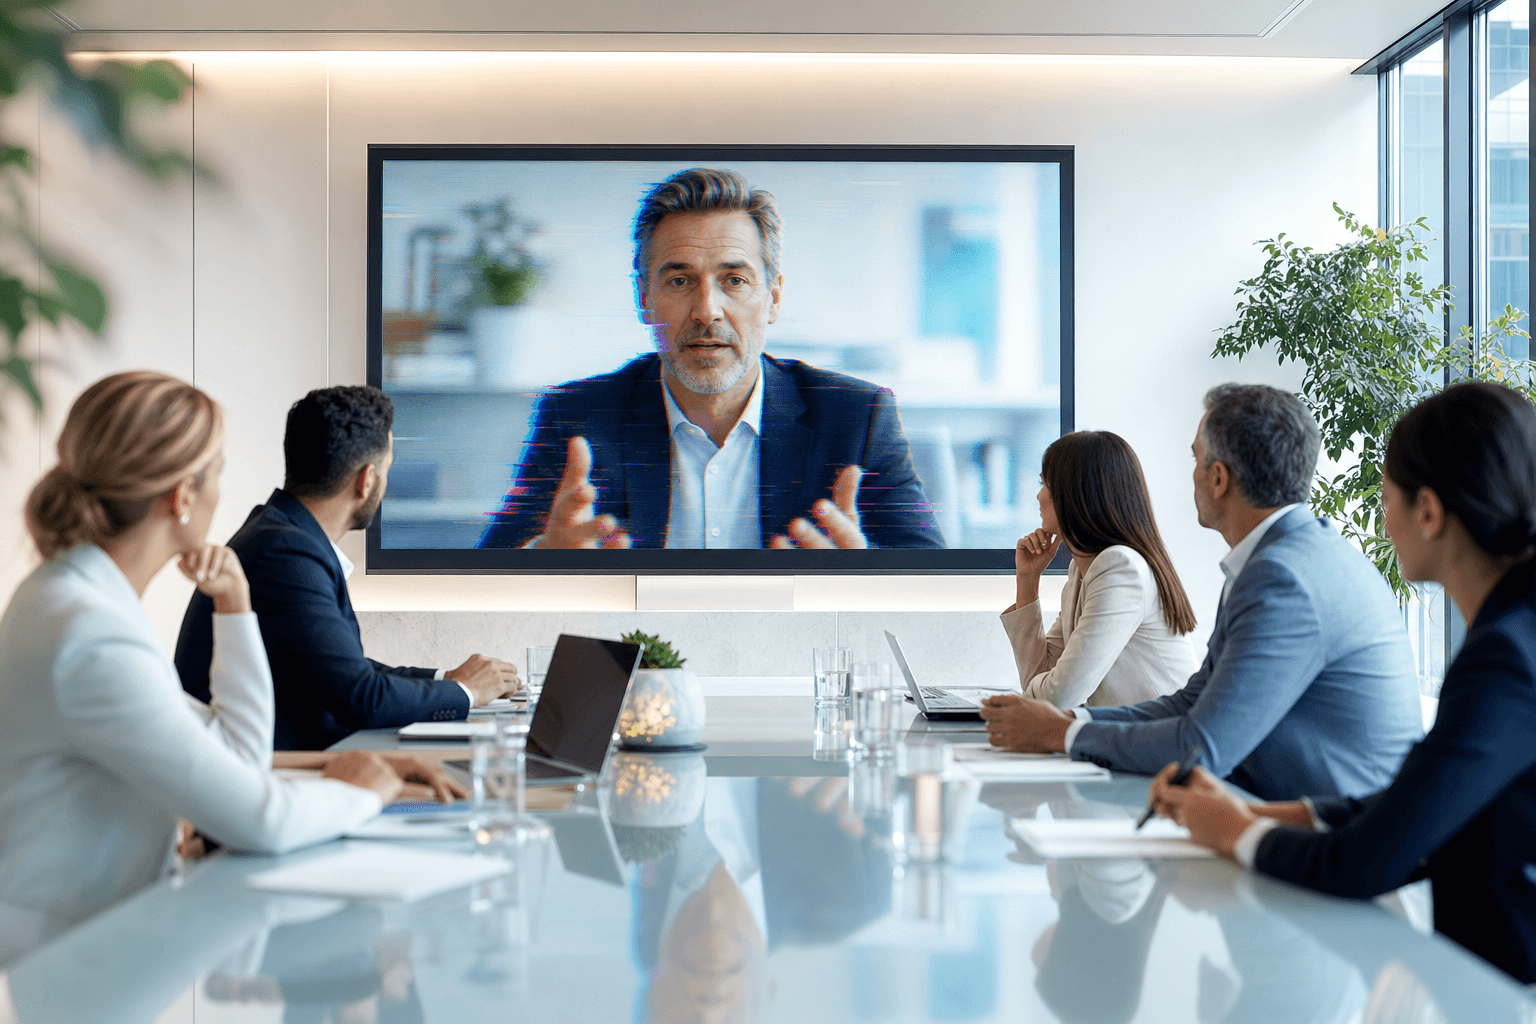
The FaceStealer attack employs advanced deepfake technology to create convincing video calls that appear to originate from legitimate sources. Attackers use AI-driven software to mimic the facial expressions and voice patterns of trusted individuals, thereby gaining the trust of their victims. Once trust is established, the attackers manipulate victims into divulging sensitive information or authorizing fraudulent transactions.
The technical complexity of this attack lies in its ability to bypass traditional security controls. Deepfake algorithms utilize neural networks to synthesize realistic video and audio content, making detection difficult. Indicators of compromise (IOCs) for such attacks include unusual communication requests, inconsistencies in video quality, and unexpected behavioral patterns during interactions.
Security researchers have identified several open-source tools used to create deepfakes, highlighting the accessibility of such technology to cybercriminals. As organizations seek to defend against these threats, they must prioritize developing detection capabilities that can identify deepfake content in real-time.
Impact Assessment: Who Is Affected and How
The FaceStealer scheme predominantly targets industries with significant cryptocurrency transactions, including finance, technology, and e-commerce. The financial implications are substantial, with losses exceeding $400 million, but the operational consequences are equally severe. Businesses may experience disrupted operations, damaged reputations, and loss of customer trust.
Beyond financial losses, the regulatory and compliance landscape is affected as well. Organizations must navigate complex legal frameworks related to data protection and financial transactions. Compliance with regulations such as GDPR and other regional data protection laws becomes critical in the wake of such incidents.
Real-World Case Studies
One notable case involved a European financial institution where attackers used deepfake video calls to impersonate the CEO, resulting in unauthorized transfers worth millions. The incident highlighted the need for robust verification processes and the limitations of current authentication methods.
Another case in the tech sector saw attackers exploiting deepfake technology to gain access to proprietary data, leading to significant competitive disadvantages. These examples underscore the importance of continuous threat monitoring and employee training to recognize and respond to social engineering attacks.
Mitigation Strategies: Protecting Your Organization
To protect against deepfake-enabled social engineering attacks, organizations should implement a multi-layered security strategy. Immediate actions include enhancing employee awareness through regular training on recognizing social engineering tactics and deepfake content.
In the short term, companies should deploy advanced AI-based detection tools capable of identifying synthetic media. These tools can analyze video and audio content for anomalies that indicate manipulation.
Long-term strategic improvements involve integrating behavioral analytics into security systems to detect unusual interactions and communication patterns. Organizations should also consider adopting blockchain-based authentication solutions to verify the identity of communication participants.
Specific technologies such as multifactor authentication (MFA) and biometric verification can further enhance security by providing additional layers of identity validation. Configuration recommendations include implementing strict access controls and regularly updating security software to address emerging vulnerabilities.
Detection and Response
Effective detection of deepfake attacks requires a combination of technical tools and human vigilance. Security teams should monitor for signs of compromise, such as unexpected communication requests and discrepancies in video or audio quality.
Incident response procedures must be robust, facilitating quick identification and mitigation of threats. Forensic analysis is crucial in understanding the attack vectors and preventing future incidents. Organizations should establish clear protocols for reporting and responding to suspected deepfake attacks.
Expert Insights: Industry Perspective
Industry experts predict that deepfake attacks will continue to evolve, becoming more sophisticated and harder to detect. As AI technology advances, the line between real and synthetic content will blur, posing new challenges for cybersecurity professionals.
Security teams must stay ahead of the curve by investing in research and development of cutting-edge detection and prevention technologies. Collaboration among industry stakeholders will be essential in sharing knowledge and developing best practices to combat these threats.
Conclusion: Key Takeaways
The FaceStealer attack serves as a critical reminder of the growing threat posed by deepfake technology in social engineering. Organizations must adopt a proactive approach to cybersecurity, emphasizing employee training and advanced detection capabilities.
- Enhance employee awareness of social engineering tactics.
- Deploy AI-based tools to detect synthetic media.
- Integrate behavioral analytics into security systems.
- Adopt multifactor authentication and biometric verification.
- Establish robust incident response procedures.
- Invest in cutting-edge detection and prevention technologies.
By taking these key actions, organizations can better protect themselves against the evolving threat landscape and maintain the integrity of their operations.
Keep reading
Discussion
Share Your Thoughts
Loading comments...
Stay Updated
Subscribe to our newsletter for the latest cybersecurity insights, threat intelligence, and security best practices.